Aditya Agrawal @exploitprotocol
Founder @GenAISecLab. Author of @pentestbox, @appsecwiki. Occasional Bug Bounty Participant. Railfan. Defence Enthusiast. ISTP India Joined January 2013-
Tweets794
-
Followers3K
-
Following555
-
Likes2K
Remember when you first tested an XSS payload and watched JavaScript execute in the browser? 👀 Now imagine an LLM generating that payload and the application executing it because the output wasnt handled securely. 🔓 𝗪𝗲𝗹𝗰𝗼𝗺𝗲 𝘁𝗼 𝗢𝗪𝗔𝗦𝗣 𝗟𝗟𝗠𝟭𝟬: 𝗜𝗺𝗽𝗿𝗼𝗽𝗲𝗿 𝗢𝘂𝘁𝗽𝘂𝘁 𝗛𝗮𝗻𝗱𝗹𝗶𝗻𝗴. The underlying problem might feel familiar to web pentesters: untrusted data reaches a sensitive application component without proper validation, sanitization, or encoding. But with LLM-powered applications, that data comes from the model, and developers may trust it more than they should. Depending on how the application handles the output, the consequences can include: 🔴 Cross-Site Scripting (XSS) 🔴 SQL Injection 🔴 Other injection vulnerabilities For pentesters, this means looking beyond the prompt itself and examining what the application actually does with the models response. I've just released 𝗟𝗟𝗠𝟭𝟬 𝗶𝗻 𝘁𝗵𝗲 𝗳𝗿𝗲𝗲 𝗔𝗜 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗟𝗲𝗮𝗿𝗻𝗶𝗻𝗴 𝗦𝗲𝗿𝗶𝗲𝘀 on GenAI Security Lab! 🔴 𝗔𝗧𝗧𝗔𝗖𝗞 — Find and exploit vulnerabilities. 🛡️ 𝗗𝗘𝗙𝗘𝗡𝗗 — Learn how to fix them. ✅ 𝗩𝗘𝗥𝗜𝗙𝗬 — Retest and verify the fix. Ready to put your AI security skills into practice? 🔗 genaisecuritylab.com/learn-ai-secur… #AISecurity #LLMSecurity #OWASP #AppSec #Pentesting #CyberSecurity #CyberSecurityTraining #ApplicationSecurity
🚨 𝗙𝗼𝗿 𝘁𝗵𝗲 𝗳𝗶𝗿𝘀𝘁 𝘁𝗶𝗺𝗲 𝗶𝗻 𝘁𝗵𝗲 𝗰𝘆𝗯𝗲𝗿𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝘁𝗿𝗮𝗶𝗻𝗶𝗻𝗴 𝗶𝗻𝗱𝘂𝘀𝘁𝗿𝘆, @GenAISecLab 𝗶𝘀 𝗶𝗻𝘁𝗿𝗼𝗱𝘂𝗰𝗶𝗻𝗴 𝗮 𝘁𝗵𝗿𝗲𝗲-𝘁𝗶𝗲𝗿 𝗿𝗲𝗴𝗶𝗼𝗻𝗮𝗹 𝗽𝗿𝗶𝗰𝗶𝗻𝗴 𝗺𝗼𝗱𝗲𝗹 𝗱𝗲𝘀𝗶𝗴𝗻𝗲𝗱 𝘁𝗼 𝗰𝗼𝘃𝗲𝗿 𝗲𝘃𝗲𝗿𝘆 𝗰𝗼𝘂𝗻𝘁𝗿𝘆 𝘄𝗼𝗿𝗹𝗱𝘄𝗶𝗱𝗲. 🌎 Here is why this matters. Many penetration testers have to pay for their own training and certifications. Most international training platforms charge in USD. But the same $100 subscription can be affordable in one country and a significant financial burden in another. A pentester in one country shouldn't have to sacrifice a much larger share of their income to access the same training as someone living elsewhere. We are building @GenAISecLab without outside funding(bootstrapped), so we understand the challenges of making a training platform sustainable. But we also believe that where you live shouldn't determine whether you can afford to develop your cybersecurity skills. Some providers already offer regional discounts in selected markets. We wanted to take a broader approach by designing a three-tier pricing model intended to cover every country worldwide. Because cybersecurity is a global industry, and access to cybersecurity education should be global, too. ❤️ So we split our pricing into three tiers, set from income per person and local purchasing power: → Tier 1: standard pricing → Tier 2: around 20% off, for countries where the standard price is harder to reach → Tier 3: around 50% off, our lowest prices, where international training costs are the biggest barrier Every tier gets the same hands-on labs, the same learning paths and the same certifications. 🎓 𝗔𝗻𝗱 𝘁𝗵𝗲𝗿𝗲𝘀 𝗺𝗼𝗿𝗲 𝗳𝗼𝗿 𝘀𝘁𝘂𝗱𝗲𝗻𝘁𝘀! We understand that students often have limited budgets and may be paying for their education and professional development themselves. That's why were offering an 𝗮𝗱𝗱𝗶𝘁𝗶𝗼𝗻𝗮𝗹 𝟰𝟬% 𝗢𝗙𝗙 𝗳𝗼𝗿 𝘀𝘁𝘂𝗱𝗲𝗻𝘁𝘀, on top of their regional pricing. We don't believe you should have to wait until you land your first cybersecurity job to afford the training that could help you get there. Read complete story at : genaisecuritylab.com/blog/fair-regi… 🔗 Explore GenAI Security Lab: genaisecuritylab.com #CyberSecurity #AISecurity #Pentesting #CyberSecurityTraining #ApplicationSecurity #AppSec
🚨 𝗥𝗔𝗚-𝗯𝗮𝘀𝗲𝗱 𝗮𝘁𝘁𝗮𝗰𝗸𝘀 𝗮𝗿𝗲 𝗰𝗼𝗺𝗺𝗼𝗻, 𝘆𝗲𝘁 𝗼𝗳𝘁𝗲𝗻 𝗼𝘃𝗲𝗿𝗹𝗼𝗼𝗸𝗲𝗱 𝗱𝘂𝗿𝗶𝗻𝗴 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝘁𝗲𝘀𝘁𝗶𝗻𝗴. Our 𝗣𝗮𝗿𝘁 𝟱 𝗼𝗳 𝘁𝗵𝗲 𝗙𝗥𝗘𝗘 𝗔𝗜 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗦𝗲𝗿𝗶𝗲𝘀 is now live at genaisecuritylab.com/learn, covering 𝗢𝗪𝗔𝗦𝗣 𝗟𝗟𝗠𝟬𝟵: 𝗩𝗲𝗰𝘁𝗼𝗿 𝗮𝗻𝗱 𝗘𝗺𝗯𝗲𝗱𝗱𝗶𝗻𝗴 𝗪𝗲𝗮𝗸𝗻𝗲𝘀𝘀𝗲𝘀. 🔥 A vector database retrieves content based on similarity. But it doesn't inherently know who should access that content, who created it, or whether it should have been deleted. 𝗧𝗵𝗶𝗻𝗸 𝗼𝗳 𝗶𝘁 𝗮𝘀 𝗯𝗿𝗼𝗸𝗲𝗻 𝗮𝗰𝗰𝗲𝘀𝘀 𝗰𝗼𝗻𝘁𝗿𝗼𝗹, 𝘄𝗶𝘁𝗵 𝗮 𝘀𝗶𝗺𝗶𝗹𝗮𝗿𝗶𝘁𝘆 𝘀𝗲𝗮𝗿𝗰𝗵 𝘄𝗵𝗲𝗿𝗲 𝘁𝗵𝗲 𝗼𝗯𝗷𝗲𝗰𝘁 𝗜𝗗 𝘂𝘀𝗲𝗱 𝘁𝗼 𝗯𝗲. 👀 This week, were covering 𝟳 𝗵𝗮𝗻𝗱𝘀-𝗼𝗻 𝗹𝗲𝘀𝘀𝗼𝗻𝘀 exploring six ways RAG pipelines can go wrong: 🔓 𝗖𝗿𝗼𝘀𝘀-𝘁𝗲𝗻𝗮𝗻𝘁 𝗱𝗮𝘁𝗮 𝗹𝗲𝗮𝗸𝘀 through improperly scoped retrieval. 🎯 𝗦𝗲𝗻𝘀𝗶𝘁𝗶𝘃𝗲 𝗱𝗮𝘁𝗮 𝗲𝘅𝗽𝗼𝘀𝘂𝗿𝗲 through overly broad search results. 💉 𝗗𝗼𝗰𝘂𝗺𝗲𝗻𝘁 𝗽𝗼𝗶𝘀𝗼𝗻𝗶𝗻𝗴 that manipulates answers for future users. 📄 𝗥𝗮𝗻𝗸𝗶𝗻𝗴 𝗺𝗮𝗻𝗶𝗽𝘂𝗹𝗮𝘁𝗶𝗼𝗻 that makes untrusted content outrank official sources. 🗑️ 𝗦𝘁𝗮𝗹𝗲 𝗱𝗮𝘁𝗮 𝗲𝘅𝗽𝗼𝘀𝘂𝗿𝗲 through indexes or caches that still serve deleted content. 🕵️ 𝗛𝗶𝗱𝗱𝗲𝗻 𝗿𝗲𝘁𝗿𝗶𝗲𝘃𝗮𝗹 𝗽𝗮𝘁𝗵𝘀 that bypass access controls through parent expansion, agent follow-ups, HyDE, hybrid search, and fallback logic. 🛡️ 𝗧𝗵𝗲 𝗳𝗶𝘅: Enforce authorization in code at query time across every retrieval path. 𝗥𝗲𝗺𝗲𝗺𝗯𝗲𝗿: 𝗬𝗼𝘂𝗿 𝗟𝗟𝗠𝘀 𝘀𝘆𝘀𝘁𝗲𝗺 𝗽𝗿𝗼𝗺𝗽𝘁 𝗶𝘀 𝗻𝗼𝘁 𝗮𝗻 𝗮𝗰𝗰𝗲𝘀𝘀 𝗰𝗼𝗻𝘁𝗿𝗼𝗹 𝗺𝗲𝗰𝗵𝗮𝗻𝗶𝘀𝗺. 💻 𝗟𝗲𝗮𝗿𝗻 𝗮𝗻𝗱 𝗽𝗿𝗮𝗰𝘁𝗶𝗰𝗲 𝗳𝗼𝗿 𝗙𝗥𝗘𝗘: ✅ No sign-up required to read the lessons. ✅ Hands-on labs with live, sandboxed targets. ✅ Free account for access to free labs. 📅 Next Tuesday: 𝗟𝗟𝗠𝟭𝟬 — 𝗜𝗺𝗽𝗿𝗼𝗽𝗲𝗿 𝗢𝘂𝘁𝗽𝘂𝘁 𝗛𝗮𝗻𝗱𝗹𝗶𝗻𝗴. #AISecurity #LLMSecurity #RAG #OWASP #AppSec #Pentesting

On an AI pentest, the system prompt is your recon. It tells you the tools, the rules and the guardrails before you send a single payload. Part 4 of my free AI security series is live: 𝗛𝗶𝗱𝗱𝗲𝗻 𝗖𝗼𝗻𝘁𝗲𝘅𝘁 𝗘𝘅𝗽𝗼𝘀𝘂𝗿𝗲 (𝗢𝗪𝗔𝗦𝗣 𝗟𝗟𝗠𝟬𝟴). LLM08 is about getting an assistant to give up what sits behind it: its instructions, its tool definitions, its guardrail rules. For a tester, that is the map for everything you try next. Live now at genaisecuritylab.com/learn Five ways it happens: • 𝗗𝗶𝗿𝗲𝗰𝘁 𝗲𝘅𝘁𝗿𝗮𝗰𝘁𝗶𝗼𝗻 - you ask the assistant to repeat or list its instructions. Do not reveal this is a request, not a control. • 𝗧𝗿𝗮𝗻𝘀𝗳𝗼𝗿𝗺𝗮𝘁𝗶𝗼𝗻 𝗮𝗻𝗱 𝗲𝗻𝗰𝗼𝗱𝗶𝗻𝗴 - a translate or reformat task reproduces the hidden setup in a form an exact-match filter does not recognise. • 𝗣𝗿𝗶𝗺𝗶𝗻𝗴 𝗮𝗻𝗱 𝗳𝗼𝗿𝗴𝗲𝗱 𝘁𝘂𝗿𝗻𝘀 - a model completes text, so a primed sentence opening gets the setup echoed back. • 𝗙𝗮𝗸𝗲 𝗺𝗼𝗱𝗲𝘀 𝗮𝗻𝗱 𝗯𝗼𝗿𝗿𝗼𝘄𝗲𝗱 𝗮𝘂𝘁𝗵𝗼𝗿𝗶𝘁𝘆 - claim a debug session or an audit, and disclosure becomes the task. • 𝗜𝗻𝗱𝗶𝗿𝗲𝗰𝘁 𝗹𝗲𝗮𝗸𝗮𝗴𝗲 - the instruction is planted in a document the assistant retrieves for someone else. The important part is what you tell the client. You cannot make a model keep a secret it can read. So the fix is to stop putting secrets there: keys, internal URLs and business rules belong in code and in server-side checks, not in the prompt. Assume the system prompt will be read, and make sure nothing breaks when it is. If you have ever found credentials in client-side JavaScript, this will feel familiar. Same mistake, new place. Five short lessons, each with a live target to try it on. Free to read and try our free labs, no paywall. Next Tuesday, 𝗢𝗰𝘁𝗼𝗯𝗲𝗿 𝟭𝟯: 𝗟𝗟𝗠𝟬𝟵 𝗩𝗲𝗰𝘁𝗼𝗿 amp; 𝗘𝗺𝗯𝗲𝗱𝗱𝗶𝗻𝗴 𝗪𝗲𝗮𝗸𝗻𝗲𝘀𝘀𝗲𝘀, covering the RAG stack itself: embedding inversion, cross-tenant retrieval, and poisoned indexes. #LLMSecurity #Pentesting #AISecurity #AppSec #CyberSecurity #GenAISecurity #AI #GenAI

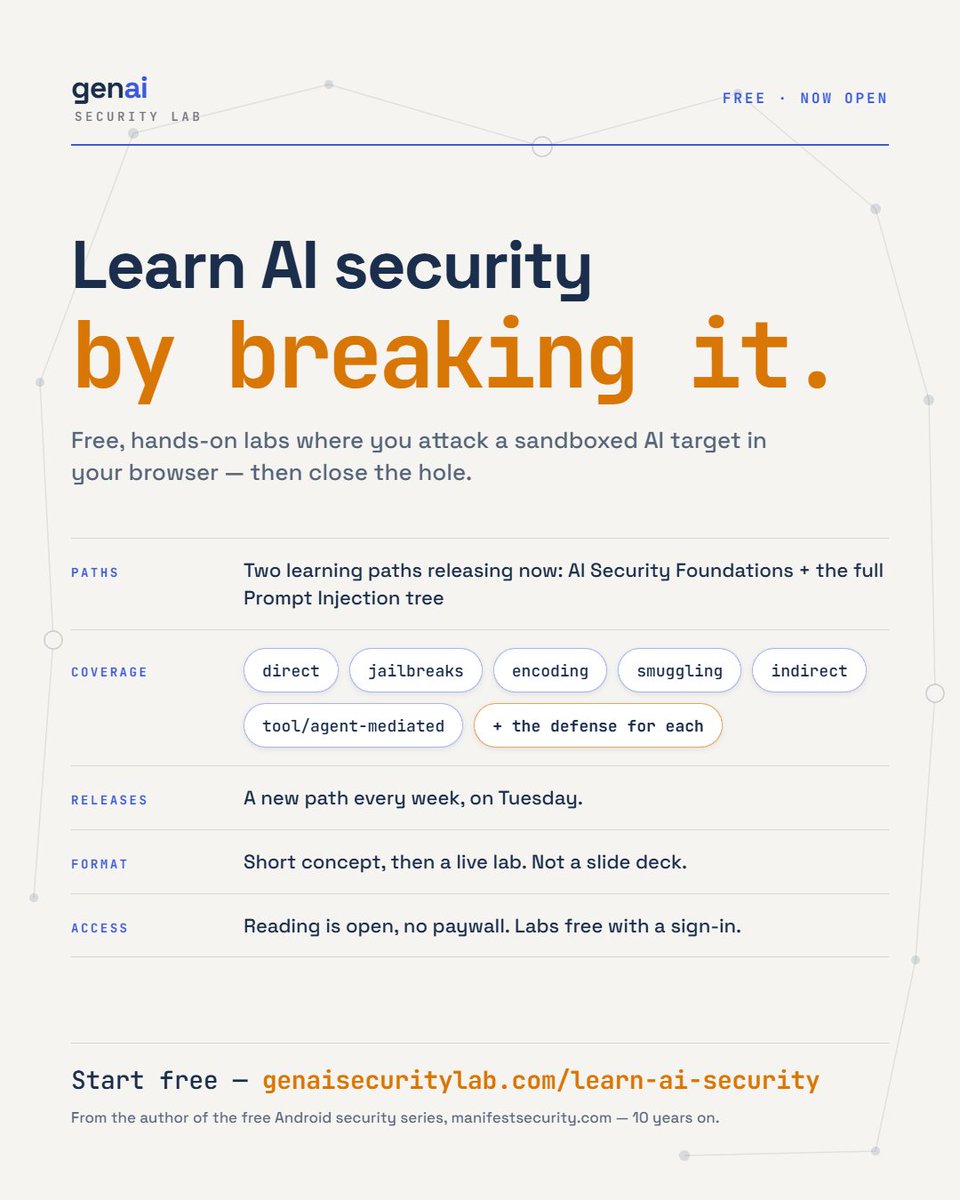
Ten years ago I published a free Android application security series at manifestsecurity(dot) com/android-application-security. At the time, Android security had almost no free material to learn from — web security had plenty. That gap is why I wrote it. It still gets traffic today, and people still message me saying it's how they learned Android pentesting. AI security has that same gap right now. So I'm rebuilding it — this time for AI. genaisecuritylab.com/learn is live. It teaches LLM security the way you'd actually test it. Short concept material, then live labs in your browser where you run the full loop: Attack → Defend → Verify. You exploit a real target, implement the fix, and verify the fix holds. Every topic has an offensive and a defensive track. It's a live system you break with your own hands — not a module you click through. Two are live today: AI Security Foundation, and Prompt Injection start to finish — direct, jailbreaks, encoding, smuggling, indirect, tool/agent-mediated, and the defense for each. Over the next 12 weeks I'll publish the rest free, one part a week, for pentesters and AppSec engineers who already know web and need to add AI to their scope: • System prompt and secret extraction • RAG data leakage and cross-tenant bleed • Agent and MCP tool abuse, excessive agency • Improper output handling → second-order injection The point: applications are shipping with LLM components now, and clients are starting to ask for AI testing. This gets you ready for that. Every part maps to the OWASP LLM Top 10 (2026), the Agentic Top 10, and the MCP Top 10 — and every part ends in a live hosted lab you attack right in the browser. No setup, no API keys, no Docker. Attack it, fix it, prove the fix holds. I'm picking 100 people as the founding cohort — early access to each part before it goes public, a private channel with me, and your feedback directly shaping the curriculum. If you want in, say so in the comments. I'll reply to every one and send you the link. #AISecurity #AppSec #LLMSecurity
Part 3 of this series is live today. More details at: x.com/exploitprotoco…
Part 3 of my free AI security series is live: 𝗦𝗲𝗻𝘀𝗶𝘁𝗶𝘃𝗲 𝗜𝗻𝗳𝗼𝗿𝗺𝗮𝘁𝗶𝗼𝗻 𝗗𝗶𝘀𝗰𝗹𝗼𝘀𝘂𝗿𝗲 (𝗢𝗪𝗔𝗦𝗣 𝗟𝗟𝗠𝟬𝟮). Five days ago I launched the "Learn AI Security" series with Foundations and Prompt Injection, and said I’d publish a new part every week. Here’s
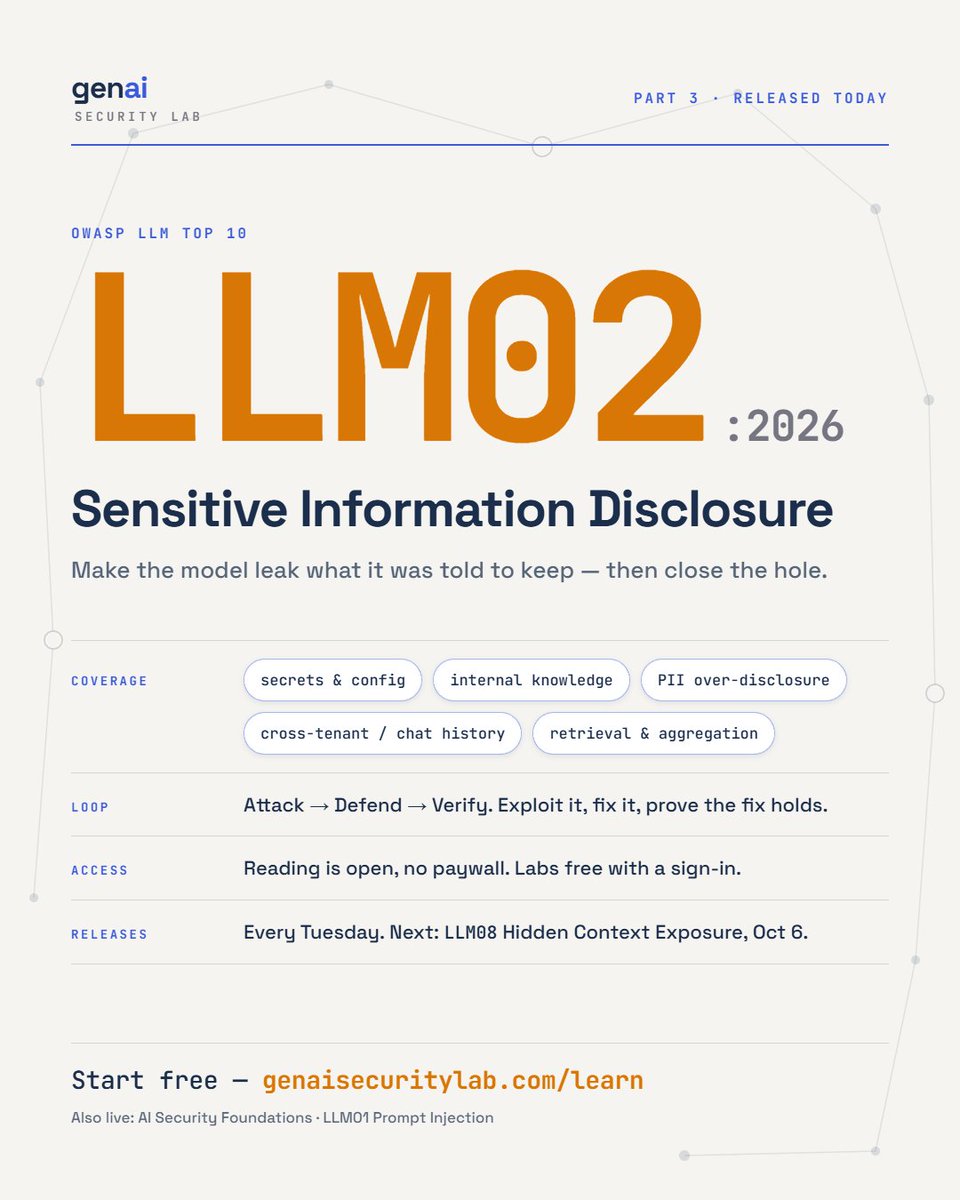
Part 3 of my free AI security series is live: 𝗦𝗲𝗻𝘀𝗶𝘁𝗶𝘃𝗲 𝗜𝗻𝗳𝗼𝗿𝗺𝗮𝘁𝗶𝗼𝗻 𝗗𝗶𝘀𝗰𝗹𝗼𝘀𝘂𝗿𝗲 (𝗢𝗪𝗔𝗦𝗣 𝗟𝗟𝗠𝟬𝟮). Five days ago I launched the "Learn AI Security" series with Foundations and Prompt Injection, and said I’d publish a new part every week. Here’s the next one. LLM02 is about situations where an AI application gives out data it was never supposed to show. Live now at genaisecuritylab.com/learn A few common examples: • 𝗦𝗲𝗰𝗿𝗲𝘁𝘀 𝗮𝗻𝗱 𝗰𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗮𝘁𝗶𝗼𝗻 exposed through the model context - API keys, internal endpoints, tool details, etc. • 𝗜𝗻𝘁𝗲𝗿𝗻𝗮𝗹 𝗸𝗻𝗼𝘄𝗹𝗲𝗱𝗴 𝗹𝗲𝗮𝗸𝗮𝗴𝗲 - staff-only runbooks, debug traces, or internal instructions being returned to users. • 𝗣𝗲𝗿𝘀𝗼𝗻𝗮𝗹 𝗱𝗮𝘁𝗮 𝗼𝘃𝗲𝗿-𝗱𝗶𝘀𝗰𝗹𝗼𝘀𝘂𝗿𝗲 - the model returns an entire customer record when the task only required one field. • 𝗖𝗿𝗼𝘀𝘀-𝘁𝗲𝗻𝗮𝗻𝘁 𝗼𝗿 𝗰𝗼𝗻𝘃𝗲𝗿𝘀𝗮𝘁𝗶𝗼𝗻-𝗵𝗶𝘀𝘁𝗼𝗿𝘆 𝗹𝗲𝗮𝗸𝗮𝗴𝗲 - one customer’s data ends up visible to another through shared context, caches, or chat history. • 𝗥𝗲𝘁𝗿𝗶𝗲𝘃𝗮𝗹 𝗮𝗻𝗱 𝗮𝗴𝗴𝗿𝗲𝗴𝗮𝘁𝗶𝗼𝗻 𝗹𝗲𝗮𝗸𝘀 - RAG retrieves restricted information, or several harmless responses can be combined to reveal something sensitive. The important part is how you defend against these issues. A system prompt saying “never reveal customer data” isn’t a reliable security control. The stronger approach is to control what gets retrieved, who is allowed to retrieve it, and what actually makes it into the model’s context. If you’ve tested IDOR and multi-tenant isolation in traditional web applications, a lot of this will feel familiar. The interesting part is learning how to actually find these issues in an LLM application. The format is the same as the previous parts: Attack→ Defend → Verify You can work through live labs directly in the browser. No setup and no API keys required. Both the attack and defense paths are free. Next Tuesday, 𝗢𝗰𝘁𝗼𝗯𝗲𝗿 𝟲: 𝗟𝗟𝗠𝟬𝟴 — 𝗛𝗶𝗱𝗱𝗲𝗻 𝗖𝗼𝗻𝘁𝗲𝘅𝘁 𝗘𝘅𝗽𝗼𝘀𝘂𝗿𝗲, covering system prompts, hidden instructions, guardrails, and other context that shouldn’t be exposed. #AISecurity #AppSec #LLMSecurity
@VickyChawla6 Great, I will share the details with you soon.
@Mohamed_Jeddah Great, I will ping you and share the details once things are finalized.
AI agents now cover most of the deterministic vulnerabilities we spent the last 15 years mastering 😄 It's made me think about how our role as pentesters and security engineers will evolve — not because those skills are gone, but because AI/LLM, Agentic and MCP security are quietly moving from "specialty" to essential skill. I’ve shared a few thoughts here: genaisecuritylab.com/blog/no-nmap-f… Would love to hear your thoughts on this! 🙌

I spent years breaking systems for a living, and the only thing that ever made me better was doing it — never reading about it. AI security is about to be part of every security job, not a specialty, so I built the hands-on AI security training I always wanted. It's live today 👇 Launch week: 25% off everything with code LAUNCH25OFF — individual plans, team seats, and the certification (offer expires 10th September 2026). Community labs stay free.
Nobody got good at web security by reading about SQL injection. You got good by breaking things, then fixing them. AI security is becoming that same baseline skill — the one every pentester, AppSec engineer, and developer shipping AI features is about to be expected to have.


Hear from @exploitprotocol as he offers his perspective, as an offensive security professional, on the differences between bug hunting and pentesting. Read more: cobalt.io/blog/from-bug-…
Aditya Agrawal, Core Lead Pentester at @cobalt_io, explains how to transition from a Bug Hunter to a Pentester, the major differences encountered when transitioning, & more! 👉 Read: bit.ly/3BDp1aL #Cybersecurity #Security #Pentesting #BugHunter #Technology #InfoSec
We try and make every good experience repeatable, and then run away from the resulting boredom.
If you don’t know it, it’s because you aren’t interested in it.
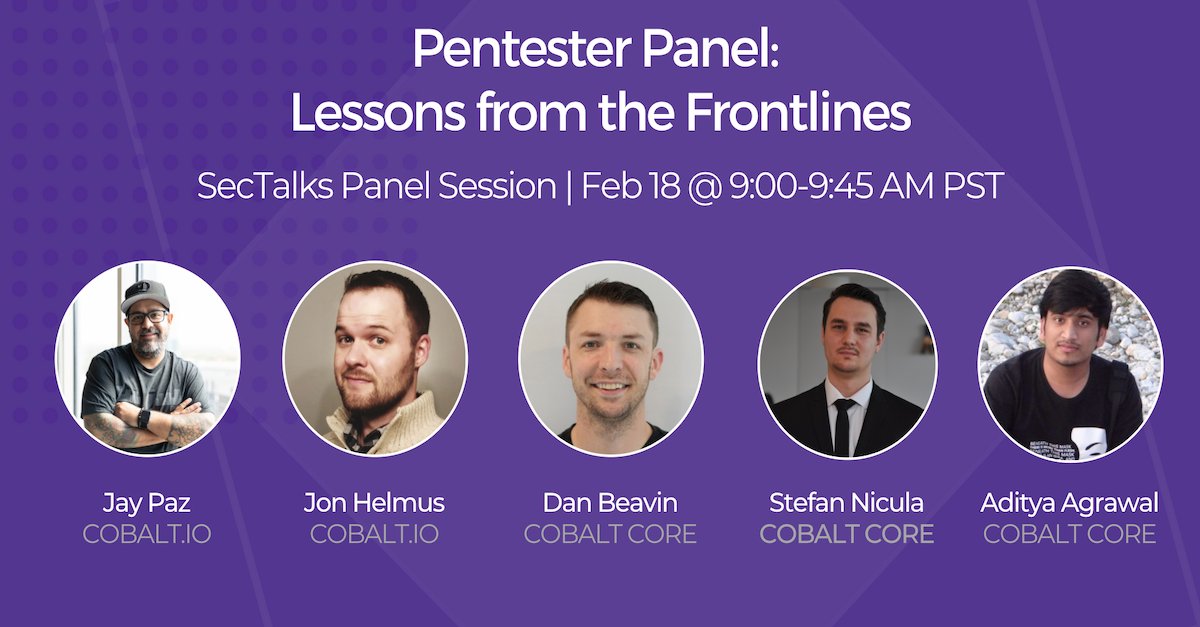
As we continue to recap sessions from our SecTalks virtual conference, check out this blog post featuring top members of the Cobalt Core (@exploitprotocol, @stefan_nicula and @danbeavin) as they bring forward key learnings from their #pentesting expertise.cobalt.io/blog/pentester…
What’s inside the mind of a #pentester? Join Cobalt’s @jjpaz and @Moos1e_Moose along with Cobalt Core members @danbeavin, @stefan_nicula and @exploitprotocol at our virtual conference on 2/18 to learn lessons from the frontlines. Register today at: hubs.ly/H0DDwxr0
Ben Sadeghipour @NahamSec
254K Followers 1K Following Cofounder @hackinghub_io | Advisor @CaidoIO. I hack companies and make content about it. #NahamCon organizer. ex @hacker0x01🇮🇷
JS0N Haddix @Jhaddix
181K Followers 7K Following CEO, Trainer, Hacker, and Speaker. Cybersecurity + Hacking + AI + Sec Leadership @arcanuminfosec
Harsh Bothra @harshbothra_
43K Followers 759 Following Freelance Pentester & Consultant • Cobalt Core Lead & Pentester • Author • Speaker • Blogger • SecurityExplained • Project Bheem • Learn365 • Views are personal
bugcrowd @Bugcrowd
205K Followers 6K Following The leading provider of crowdsourced cybersecurity solutions purpose-built to secure the digitally connected world...Unleash Ingenuity™
shubs @infosec_au
60K Followers 2K Following Co-founder, security researcher. Building an attack surface management platform, @assetnote
Shashank | CredShield... @cyberboyIndia
11K Followers 2K Following Co-Founder @credshields Ex Security Analyst @Hacker0x01 Leading https://t.co/YnFOEI7b9p
InfoSec Community @InfoSecComm
57K Followers 635 Following Largest InfoSec publication with 80,000+ followers and 3M+ monthly views.

Harsh Jaiswal @rootxharsh
28K Followers 1K Following Co-founder and research @hacktronai | auditing at @cure53berlin | prev @zomato @vimeo @pdiscoveryio @httpvoid0x2f
payloadartist @payloadartist
46K Followers 292 Following I discuss AI, Cybersecurity & Hacking • Helped secure organizations like Google • Opinions are my cat's • Part-time shitposter
Geekboy @emgeekboy
26K Followers 487 Following Hacker, Co-Founder @pdiscoveryio, Ex-Security Analyst / BugBounty @Hacker0x01
zseano @zseano
83K Followers 723 Following rebuilding https://t.co/oFH3BQm9YZ and creating zseano methodology v2. *COMING SOON!!* ex full time amazon hacker 2018-2026 🫡
Rahul Maini @iamnoooob
16K Followers 2K Following Research at @httpvoid0x2f @HacktronAI, before @pdiscoveryio
Jobert Abma @jobertabma
43K Followers 703 Following I tweet about security and my experience as a hacker. Co-founder of HackerOne (@Hacker0x01).
Pentester Academy @SecurityTube
199K Followers 14K Following We help professionals acquire the skills, knowledge and certificates by teaching defense through offense to advance their careers in cybersecurity.
Mobile Security @mobilesecurity_
31K Followers 1K Following Mobile Security ✌🏻 #MobileSecurity #AndroidSecurity #iOSsecurity

Aseem Shrey @AseemShrey
9K Followers 4K Following Infrastructure Security Engineer @Scale_AI 🏗️ Building https://t.co/kOyHkqQceM & https://t.co/4VLfZFaNTN Prev. https://t.co/uFfUUZrWvp #cybersecurity #AIsecurity

EnviHoz8 @EnviHoxha
1 Followers 161 Following
felipefrancosec @felipefrancosec
76 Followers 138 Following 👨🏻💻 Cybersecurity & Ethical Hacking 💎 Pentest • Red Team • Bug Bounty • CTFs 🧠 Aprendendo, quebrando e explicando segurança 💻 Labs, projetos e conteúdo
0xFF @streamTheBlob
11 Followers 139 Following Frontend Engineer with 5+ years of experience. Exploring web security, vulnerability research, and bug bounty hunting.
Sky Grip @skygrip777
15 Followers 2K Following
Chloe Bennett @audiee_ai
505 Followers 730 Following Co-founder @audiee_ai 🧠 giving AI agents persistent local memory 🎙️ AI meeting notes that never join the call 🎓 Brown alum · 📍 SF · 🚢 shipping daily

orvalho @orvalhoDev
118 Followers 861 Following
Hira Jha @MaiHoonHira
27 Followers 395 Following Built https://t.co/Ycu5NoL3Tl and https://t.co/RPf49gwIAr, a trust intelligence API. Algo & F&O trader, own AI trade systems. I write about tech, AI and what I break.
Het Mehta @hetmehtaa
43K Followers 2K Following Security Engineer | Content Creator | I talk about Cybersecurity, Tech, Privacy, AI & Startups | Building @Sentynio @100xSecurity
Pentest Box @pentestbox
1K Followers 2 Following An Opensource PreConfigured Portable Penetration Testing Environment for the Windows Operating System. Made by @exploitprotocol
Empty Mind @sad_butsmile_7
130 Followers 2K Following Im Muslim || Cyber Security Researcher | Bug Bounty Hunter | Blogger | Domainer
Eric @Ericddo_
1 Followers 817 Following
TanmayLP @TanmayLP7
373 Followers 3K Following LPT (Master) | CPENT | CEH Security (Web | API | AI) जे जितकं, जेव्हा जसं ते तितकंच, तेव्हाच तसंच ||


Dmitry Alimov @dmitryalimov
37K Followers 39K Following Tech VC and entrepreneur. Curious. Investing and building in AI. Built tech and media companies. Founder @frontiervc. Learned things @Harvard, @Stanford
GenAI Security Lab @GenAISecLab
11 Followers 2 Following Hands-on AI security training. Exploit real LLM, RAG, MCP and agent flaws in isolated labs, then watch the grader replay your attack against the fix.
Babyf0li0_ @bebyfolio
22 Followers 2K Following Software Engineer managing a $6M+ portfolio to build generational wealth for my 2 babies. Covering Al infrastructure, Semis and Datacenters
Tiesna Sulistiana | J... @jurnalsenamyid
5K Followers 3K Following SEO Specialist • Graphic Designer • Website Developer • AI Enthusiast • ✍🏻 at @jurnalsena | Sometimes reading a book, sometimes making a game at @cyberusstudio
agrawal sanskar @agrawalsanskar5
109 Followers 2K Following

Indian Vibes @IndianVibeDaily
3K Followers 6K Following Daily updates on India | Trends, memes & viral moments 🇮🇳


Alan Analista @AlanAnalista
220 Followers 830 Following Analista de sistemas, Amigo e Blogueiro. De volta em nova fase. #Android
Akash Biswas @akashbiswas_81
0 Followers 63 Following

Nayeem @Asm_Nayeem5
2 Followers 59 Following
the storm trooperson @stormtrooperson
707 Followers 4K Following Just another renegade stormtrooper fighting against the BolsoPetismo
Abhishek Malviya @IamAbhishek_97
7 Followers 214 Following Cybersecurity Researcher 🇮🇳 || Bug Bounty Hunter ||
Agrasen Jayanti @AgrasenJayanti
9 Followers 321 Following Maharaja Agrasen’s Principle of “One Brick, One Rupee” (एक ईंट, एक रुपया)

Raghunandan Sharma @raghu__79
38 Followers 66 Following
Sumanta Kumar @YtoDark
51 Followers 2K Following Hello 👋 This is Sumanta Kumar I am Both Blackhat & Whitehat Hacker,Penitration Tester,Bug Hunter,Web Developers.hobby is traveling for country to country.
Dharmik._.777 @dharmikkk_777
3 Followers 454 Following


Nightvale @Nightval7
2 Followers 213 Following
Erslaswaw @Erslaswaw0715
0 Followers 49 Following


ig02it @wseiyze
0 Followers 143 Following
Dharaniraj Sekar @NirajArahD
0 Followers 124 Following
Valeriy @Krevetk0Valeriy
6K Followers 935 Following Security enthusiast, bug bounty hunter at @Hacker0x01 and @Bugcrowd https://t.co/RjYvPJaXTW https://t.co/dkUfA2vywe
Ben Sadeghipour @NahamSec
254K Followers 1K Following Cofounder @hackinghub_io | Advisor @CaidoIO. I hack companies and make content about it. #NahamCon organizer. ex @hacker0x01🇮🇷
JS0N Haddix @Jhaddix
181K Followers 7K Following CEO, Trainer, Hacker, and Speaker. Cybersecurity + Hacking + AI + Sec Leadership @arcanuminfosec
Harsh Bothra @harshbothra_
43K Followers 759 Following Freelance Pentester & Consultant • Cobalt Core Lead & Pentester • Author • Speaker • Blogger • SecurityExplained • Project Bheem • Learn365 • Views are personal
bugcrowd @Bugcrowd
205K Followers 6K Following The leading provider of crowdsourced cybersecurity solutions purpose-built to secure the digitally connected world...Unleash Ingenuity™
Julien | MrTuxracer �... @MrTuxracer
40K Followers 441 Following CEO @rcesecurity | #BugBounty | @Hacker0x01 MVH && H1-Elite | $1,5+ Mio in Bounties | Mobile Hacker | @[email protected]
Joseph Thacker @rez0__
75K Followers 1K Following christian. father. hacker. founder. advisor. podcast: https://t.co/1aFavJN2h8 blog: https://t.co/JBPT1CJWJH products: 💻 https://t.co/iPdpsEAc1h 🤖 https://t.co/EVhQl8HTlp 📚 https://t.co/MMmhw0cnaz
shubs @infosec_au
60K Followers 2K Following Co-founder, security researcher. Building an attack surface management platform, @assetnote
Shashank | CredShield... @cyberboyIndia
11K Followers 2K Following Co-Founder @credshields Ex Security Analyst @Hacker0x01 Leading https://t.co/YnFOEI7b9p
Yassine Aboukir 🐐 @Yassineaboukir
34K Followers 424 Following HackerOne Top 40, Elite, Pentest Lead, Ambassador, x2 MVH Title, and ex- Hacker Advisory Board • Digital Nomad/Hybrid Athlete/Surfer
Corben Leo @hacker_
72K Followers 872 Following
Nate @nnwakelam
44K Followers 1K Following
Harsh Jaiswal @rootxharsh
28K Followers 1K Following Co-founder and research @hacktronai | auditing at @cure53berlin | prev @zomato @vimeo @pdiscoveryio @httpvoid0x2f
payloadartist @payloadartist
46K Followers 292 Following I discuss AI, Cybersecurity & Hacking • Helped secure organizations like Google • Opinions are my cat's • Part-time shitposter
Gareth Heyes \u2028 @garethheyes
40K Followers 1K Following Web security researcher at PortSwigger. Author of JS for Hackers and Hackvertor. https://t.co/akVN6ZR4C8
Geekboy @emgeekboy
26K Followers 487 Following Hacker, Co-Founder @pdiscoveryio, Ex-Security Analyst / BugBounty @Hacker0x01
Binni Shah @binitamshah
140K Followers 159 Following Linux Evangelist, Malwares, Security enthusiast ,Investor,World Economy, Finance,Contrarian , Philanthropist , Reformist , Sigma female [email protected]
James Kettle @albinowax
85K Followers 106 Following Director of Research at @PortSwigger. Startup advisor. Find my research, tools & contact details at https://t.co/vP6UbGmvl3
publiclyDisclosed @disclosedh1
68K Followers 2 Following This is an unofficial HackerOne public disclosure watcher who keeps you up to date about the recently disclosed bugs. By @NOBBD
zseano @zseano
83K Followers 723 Following rebuilding https://t.co/oFH3BQm9YZ and creating zseano methodology v2. *COMING SOON!!* ex full time amazon hacker 2018-2026 🫡
Rahul Maini @iamnoooob
16K Followers 2K Following Research at @httpvoid0x2f @HacktronAI, before @pdiscoveryio
Robby Frank @RobbyFrank
8K Followers 63 Following I scale companies with AI and paid ads. $5M+ ARR 📈 Co-founder of https://t.co/z2mRjzV1gl, https://t.co/OnHkKmIcE6 (#3 on TrustMRR), https://t.co/CFqR7LG3yw & more Happily married w/ 4 kids
Aseem Shrey @AseemShrey
9K Followers 4K Following Infrastructure Security Engineer @Scale_AI 🏗️ Building https://t.co/kOyHkqQceM & https://t.co/4VLfZFaNTN Prev. https://t.co/uFfUUZrWvp #cybersecurity #AIsecurity

Pratik Dabhi @impratikdabhi
19K Followers 1K Following 👨🏻💻Ethical Hacker 🐞Bug Hunter | Penetration tester 👨🏻💻Senior Security Consultant Bugcrowd Top 300 | YouTuber (23k+ Subs) | Yeswehack Top 100
Ansh Bhawnani @techhacker98
10K Followers 85 Following Information Security Researcher and a student.
Rohan Gotwal @rohangotwal
2K Followers 645 Following Senior Frontend Dev turning into an indie hacker SaaS - https://t.co/zMjt1wwr25 https://t.co/2UFdiLIlGg D2C Brand - https://t.co/BRlkDeZOEl($100k+ ARR)
Kanisshka @kanisshka12
1K Followers 1K Following Quit 9-5 to grow - https://t.co/iR6YrAlVbG https://t.co/0EMvGJth0T & https://t.co/W16ZRUP9vI Ex-software engineer → Solo SaaS builder
Deepak Dhiman🇮🇳 @Virdoex_hunter
8K Followers 405 Following bbhunter-virdoexhunter^ | Top 10 on hackenproof | Top 5 as Indian | X-Bounty Hunter Inspiration:Stok,Aditya
Harley Kimball @infinitelogins
8K Followers 1K Following Researcher Strategy & Live Hacking @ HackerOne | Community Cultivator | Bug Bounty Hunter | Co-Founder of @BugBountyDEFCON | Founder of Disclosed Newsletter.
Mohamed ~ @Mohamed_Jeddah
3K Followers 3K Following #100Devs Software Engineer https://t.co/YCwkTtQ9A0 https://t.co/sNuC94KnPp https://t.co/i5nXJkRHtK https://t.co/cIGkXtwAud (pls DM to confirm)
Marius du Preez @mdp_sec
4K Followers 350 Following Building BB Arena: which AI models can really hack? https://t.co/vOXBILNHDr Full-time bug bounty hunter on @Hacker0x01 @Bugcrowd 600+ reports, 150 critical
Het Mehta @hetmehtaa
43K Followers 2K Following Security Engineer | Content Creator | I talk about Cybersecurity, Tech, Privacy, AI & Startups | Building @Sentynio @100xSecurity
Priyam Raj @priymrj
16K Followers 2K Following building on internet since 2016 Founder https://t.co/Zled1bgO1d ($70k/mo) https://t.co/ckjJhqBlsl ($45k/mo) @warpexit 2x exits 🏆
GenAI Security Lab @GenAISecLab
11 Followers 2 Following Hands-on AI security training. Exploit real LLM, RAG, MCP and agent flaws in isolated labs, then watch the grader replay your attack against the fix.
Charles @charleslayerr
2K Followers 195 Following I have scaled https://t.co/6JqGV5CnsZ to +1M views/week, 5k subs, +24k followers @CarlosMoralesG_ Vibe Growth Marketer @zernio (+5M$ ARR)
Dmitry Alimov @dmitryalimov
37K Followers 39K Following Tech VC and entrepreneur. Curious. Investing and building in AI. Built tech and media companies. Founder @frontiervc. Learned things @Harvard, @Stanford
Fraser @iamfra5er
19K Followers 790 Following Founder of a $8M ARR startup. Build ai agents people will pay for https://t.co/OjwEJWyvU6
Tibo @tibo_maker
215K Followers 3K Following 📽 https://t.co/OyNJ8ZUyOh 📈 https://t.co/JkVOl1O0S1 🤖 https://t.co/tywwX4TyWa https://t.co/EFUcKeBbpU https://t.co/KG9PgxJabg https://t.co/1MEIhy0L5K https://t.co/jS9GQJ5Ps8 sold Tweet Hunter, Taplio ($10m) PH Maker of Year 🥇 growth tips: https://t.co/ereQodN3Ov
Romàn @romanbuildsaas
22K Followers 309 Following Co-Founder & GTM @gojiberryai (YC P26) | Building AI agents that find & book meetings with your next customers | 3500 customers | 1x exit
John @hello_code_
3K Followers 2K Following Building profitable AI SaaS in public https://t.co/9N6OAcmsPr • AI search visibility https://t.co/PZN309nKtB • Reddit & X customer leads
Jonathan Geiger @JonathanGeige18
2K Followers 356 Following Developer and founder who enjoys building products :) Sold SocialKit, CaptureKit, LectureKit. Currently building https://t.co/UijvOrlhJh & https://t.co/u8EfyKgYzg

jack friks @jackfriks
181K Followers 2K Following curious guy creating things @ https://t.co/HXWladih08 - up and coming wife guy


TrustMRR @trust_mrr
11K Followers 14 Following 🛡️ The $1.5B database of verified startup revenues 🤝 Buy & Sell: https://t.co/F21O1ibYQQ 👀 "@trust_mrr verify" to expose scammers
Martin Voelk @martinvoelk
10K Followers 1K Following Co-Founder & Chief Research Officer @ https://t.co/fa5pMEjISn | CISSP • OSCP • CCIE • BSCP • AIRTP+ | Redefining AI powered Red Teaming | Husband | Dog dad
ClaudeDevs @ClaudeDevs
764K Followers 2 Following Official updates for developers building with @ClaudeAI
Babyfolio @babyfolio
61K Followers 596 Following Software engineer & Investor for 10+ years managing generational wealth for my 2 babies. Covering AI infrastructure. ↓ My Portfolio & Real-time Trade Alerts ↓
YeahDave @Yeah_Dave
34K Followers 459 Following Space | Energy | Defense | AI | Quantum | Finance | Posts are for education & discussion, never investment advice. The market pays me, I share everything freely
TheApeOfGoldStreet @TheApeOfGoldST
24K Followers 478 Following 🇸🇪Former poker professional turned Gold and Silver bull. Nothing I share is financial advice. DYOR.
Northstar @NorthstarCharts
171K Followers 713 Following Military meteorologist. Applying scientific, predictive principles to forecast market movements. Macro economics & trading. A picture paints a thousand words.
JustDario @DarioCpx
121K Followers 397 Following Entrepreneur | Angel Investor | Asymmetric Bets | Many opinions on Macro, Stocks, and Facts | My Slice Portal for market professionals: https://t.co/76NYEoFoj2
Dinesh Arya @DineshArya_Algo
2K Followers 86 Following 💹 Full-Time Profitable Trader 😎 || 🔥 Passionate Market Explorer ||🧠 Algo Architect & Market Analyst || 📈 Trading Index, Crypto & Commodities Since 2019 🚀
V @VWAPmag
2K Followers 306 Following participant | USD down 'modities up | supply chain logistics & manufacturing | theres an asset called XMR | father of the dreaded "16 year cycle theory"
CA Arvind Mangal @camangalarvind
87K Followers 3 Following FCA,SEBI Reg. Research Analyst INH000010450 https://t.co/fhfperUftR #chart_Sab_Kuch_Bolta_Hai™️Black Book to Stock Market®️Psychological Trader
Yuvraj Shah @YuvrajShah02
15K Followers 382 Following FnO Trader & Equity Investor 🇮🇳 | NISM certified Research Analyst | Not SEBI registered | 12 months verified PnL ⬇
Rob Hallam @robj3d3
67K Followers 2K Following Shipping like a machine while I travel the world 🌍 👀 https://t.co/izXGPE0Pte $45K/mo 🔥 https://t.co/myyLdxW71O $22K/mo 🤖 https://t.co/VrHuzoNM9B $13K/mo 🚀 https://t.co/5fSvUf0gY7 $38K
skull @brutecat
9K Followers 413 Following security @google. 21. i run a blog @ https://t.co/cBW6gzSS5u
John Mackey @iamjohnmackey
4K Followers 51 Following Entrepreneur, Author, Conscious Capitalist, Co-founder of Whole Foods Market, and CEO of https://t.co/YdfkihRbe7.
Ashwin Raghavan @GripFangWolf
23K Followers 1K Following US Investing Champion 2025 (5th in $1M div) | Ex PM & Founding Engineer @PhonePe | Serendipity, Intuition and Conscientiousness 🙂 | No paid advisory / courses
Critical Thinking - B... @ctbbpodcast
27K Followers 89 Following A 'by Hackers for Hackers' podcast focused on technical bug bounty content. Exploits, techniques, stories, bounties. Hosts: @rhynorater, @rez0__, @gr3pme
DeepValue Signals @DVSignals
17K Followers 115 Following 25+ yrs in markets. Macro, deep value, niche commodities. Early on overlooked plays. Charts + context → conviction. Trading: https://t.co/sYZPBI22ri
Peter Grandich @PeterGrandich
24K Followers 101 Following Part of a financial planning group in Wall, NJ, blogger and podcaster https://t.co/83329J2UYi https://t.co/gW5R0QBFvV
First Squawk @FirstSquawk
573K Followers 251 Following Firstsquawk Is a Global Financial (News) Squawk Service Specialising In Financial Markets, Macro, Geopolitics,politics

KAZ @ralphkaz
7K Followers 965 Following All charts are my opinions only; not financial advise! If you find value in my work you can Buy me a Coffee! https://t.co/w3SCQ7fIjvYou might like