-
Tweets508
-
Followers13K
-
Following6
-
Likes79

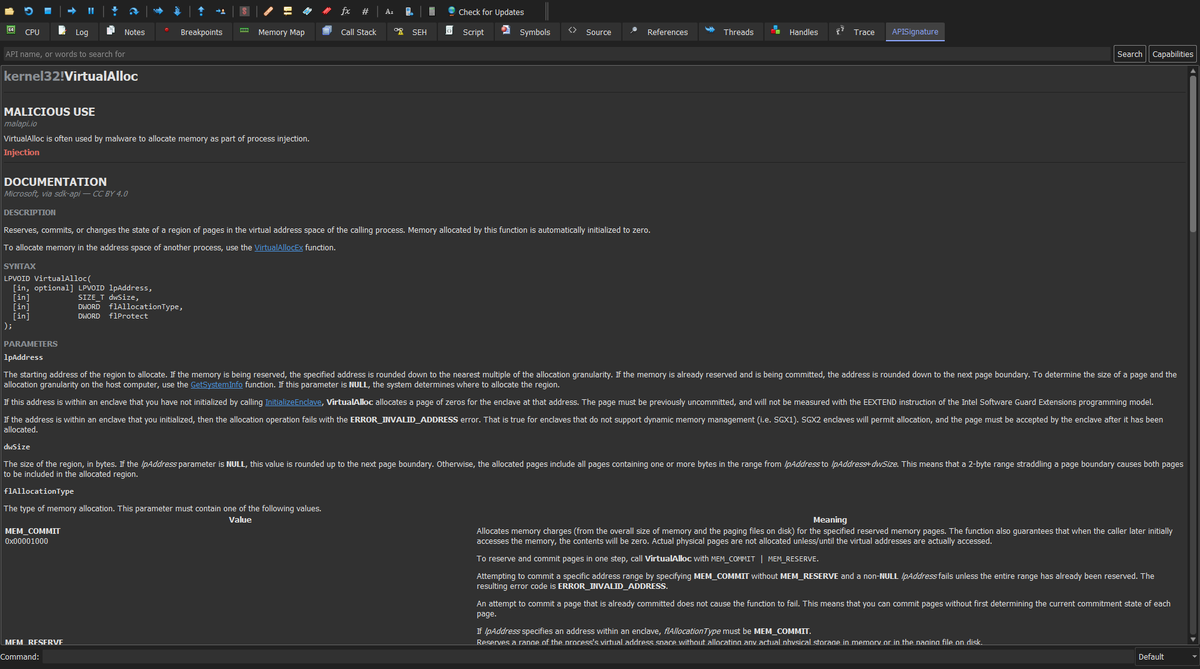
During my SANS 598 course I built a project that solves a real pain point for me as a malware analyst. I kept leaving the debugger to look up an API's Microsoft documentation or how it gets abused. So I built APISignature, an x64dbg plugin: Microsoft docs, malapi abuse notes, and the capa chains detect malicious patterns an API belongs to. 44,000+ APIs, offline. Plus an optional MCP server, so your AI assistant looks them up instead of guessing. github.com/mohammad-alatt…
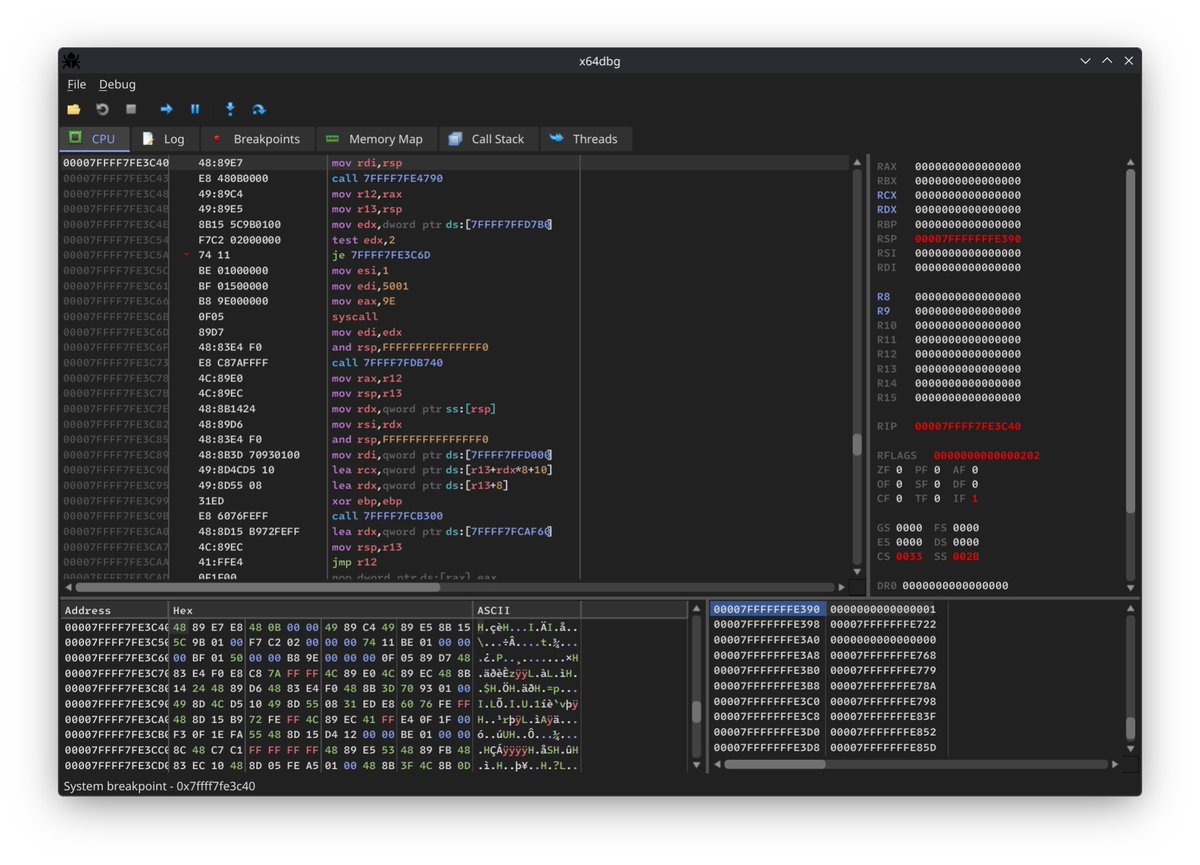
There is also a pre-alpha Linux version brewing 👀
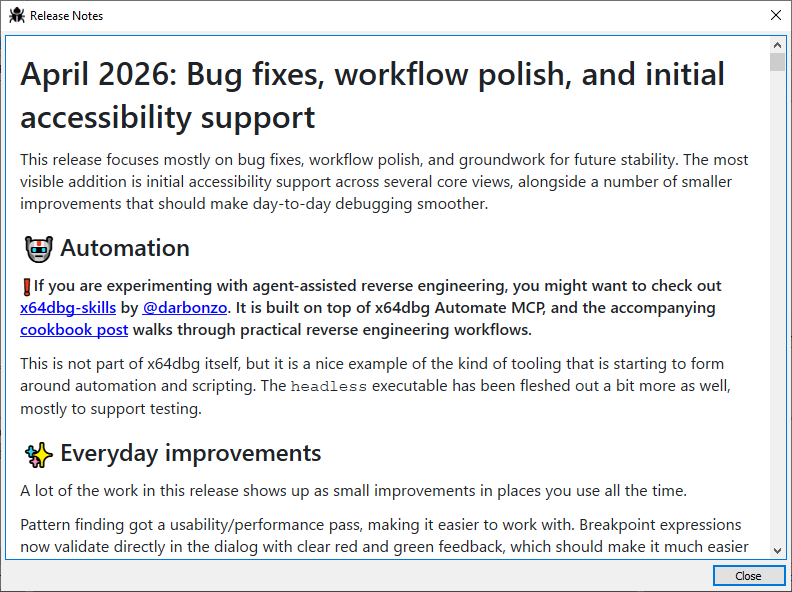

Today I published "x64dbg-skills" built on x64dbg Automate MCP. I'm *floored* how capable they are, and this is just the start 🥳 I wrote up a cookbook post that walks through using agent skills for all kinds of cool reverse engineering, check it out! x64.ooo/posts/2026-02-…
@k0ng0x86 Yeah unfortunately some pretty awful bugs slipped in 😩
New release for x64dbg is out, get it while it's hot! 🔥

Going to chat now with Josh about the recent x64dbg updates, might be interesting for people here! youtube.com/live/eODAI3Z1d…
🚀 Next live stream this Thursday - x64dbg creator Duncan Ogilvie joins the stream to talk about the latest features! Join us on YouTube -> youtube.com/live/eODAI3Z1d…
We're excited to announce a major new release of x64dbg! The main new feature is support for bitfields, enums and anonymous types, which allows all types in the Windows SDK to be represented and displayed 🔥
You can now try the ManyTypes plugin by @snowyuwa to directly parse C types and visualize them while debugging! github.com/notpidgey/Many…
It is now super easy to build x64dbg and start contributing, give it a try!🤓
@MalwareUtkonos There is no documentation needed. Just open the folder and press build 😎
@Andy6888 Wgat version of Visual Studio are you using?

Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
GuidedHacking @GuidedHacking
59K Followers 419 Following Reverse Engineering & Game Hacking Courses @ https://t.co/Dl5ED4o7YS
hasherezade @hasherezade
91K Followers 973 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
Jiří Vinopal @vinopaljiri
11K Followers 634 Following Security Researcher at @_CPResearch_ All opinions expressed here are mine only. https://t.co/bNWc3k9HwF

Hex-Rays SA @HexRaysSA
10K Followers 153 Following We are a hi-tech company focusing on binary software analysis - IDA Pro and the Hex-Rays Decompiler. ***Discourse Forum: https://community.hex-rays***
Grzegorz Tworek @0gtweet
39K Followers 2K Following My own research, unless stated otherwise. Not necessarily "safe when taken as directed". GIT d- s+: a+ C++++ !U !L !M w++++$ b++++ G-
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Ange @angealbertini
25K Followers 927 Following Reverse engineer, file formats expert. Corkami, CPS2Shock, PoC||GTFO, Sha1tered, Magika... Security engineer @ Google. He/him.
Matthew @embee_research
15K Followers 2K Following Security Researcher, Creating and Sharing Educational Content.
Josh Stroschein | The... @jstrosch
12K Followers 1K Following Reverse engineer and content creater | 😱 1M+ views on YT | 🎙️ Host of Behind the Binary podcast 👇
SEKTOR7 Institute @SEKTOR7net
17K Followers 348 Following Homo Aptus. Vincit qui se vincit - Publilius Syrus. Consulting, Training, Technology, Cyber domain, and more... @x33fcon founder.
Clandestine @akaclandestine
65K Followers 5K Following | Security | Osint | Threat Research | Opsec | Threat Intelligence | Infosec | Threat Hunting | Humint |


Richard Johnson @richinseattle
19K Followers 3K Following Computer Security, Reverse Engineering, and Fuzzing; Training & Publications @ https://t.co/mloVP6rPB7; hacking the planet since 1995; Undercurrents BOFH

Kabir Wahid @kabir_wahid78
48 Followers 5K Following
Meat Proxy | Full Tim... @brandstart87
28 Followers 375 Following Reverse Engineer Script Kiddie Im bored as hell
Luke Anthony @OrpheusTwin
51 Followers 449 Following Autonomous AI Systems Architect | LLM Integration

abderrahmene chebab @abderrahmenech1
16 Followers 477 Following
moonlit martyr @Moonkidofhate
52 Followers 1K Following Casual observer of chaos, professional architect of outcomes🌆 Tar soul🖤👾 CompTIA certified🎩
CC @AirCharlie10
79 Followers 2K Following
John Sena hehe @johnsena1102
2 Followers 133 Following
Ilia Epanov @iliaepanov
1 Followers 236 Following Certified eCPPT and eWPTX. Open to cybersecurity opportunities.
Mizuhiro @mizukaaruhiro
1 Followers 111 Following I love art, art of understanding everything Live in earth U1 No 🚫AI made with love
Alex @alexsruth
26 Followers 17 Following
Aleksandr Nameless @madgrok
52 Followers 624 Following
Artin @artinlenz
391 Followers 2K Following 🗽 Interested in the bond between tech & fitness ⚡️ Athlete (gymnastics-cyclist)🤸🚴


Alexander Ushakov @au931203
0 Followers 329 Following Individuum over socium, knowledge over individuum
Luminm @Luminmlaken
0 Followers 141 Following

nicolas @floresismoo
7 Followers 59 Following reverse engineering | low-level programming | writeups | windows internals | rust | cheat & anti-cheat developer 18 y/o | 🇦🇷


nvroot @nvroot
2 Followers 263 Following
Adolan @adolandev
908 Followers 618 Following I build things. I break things. Occasionally on purpose. Ambassador @cognition.
Chung Dinh @suff3r3d
1 Followers 150 Following
Fly_Phantom_Fly @Fly_Phantom_Fly
5 Followers 153 Following Android Enthusiast || Reverse Engineer || PhantomThreads
Mahmoud Kamal @MAHMOUDMDKAMAL
0 Followers 36 Following


B1 Cyber Security @B1Cyber
11 Followers 208 Following Information Security Specialist. Technology, Programming, Pen-testing, Reverse Engineering and Malware Analysis.
tali @nocta_li
4 Followers 73 Following

张三 @Z2021_X
1 Followers 11 Following
asher @aaddpp_vmp
620 Followers 43 Following 18 year old cyber security student out of PA. https://t.co/ag0jCNKcar https://t.co/fvlmAOgLd2
idk @Johnny91436361
1 Followers 169 Following


Sergey Quantum 📡�... @modqft
70 Followers 926 Following PhD in Theoretical Physics. Researcher in machine learning for high-energy physics (ex LHCb member). Interested in #DeSci and #cypherpunk.


Terrence Henry @Ter2ence
139 Followers 609 Following Terry's Lair Pool - TLP #SouthAfrica #Cardano #SPO Covering 4 continents and counting...
Nicholas Michael Klos... @showxlate
120 Followers 668 Following backwards engineer • developer • security researcher • ICSA-25-140-11
justAK @0x3Griff
2 Followers 108 Following
blazeinparis @blazeinparis
0 Followers 18 Following
selectedambient @parhelicsquare
0 Followers 10 Following i make tools @ https://t.co/HrNBuCGEjL https://t.co/ql3Zq7jeB6
Mateusz @VirtualParticl3
5 Followers 103 Following

Rob Vogelaar @robevogelaar
23 Followers 366 Following
Álvaro García León @AGMNTD
16 Followers 1K Following
Josh Stroschein | The... @jstrosch
12K Followers 1K Following Reverse engineer and content creater | 😱 1M+ views on YT | 🎙️ Host of Behind the Binary podcast 👇

Ryan "Chaps" Chapman @rj_chap
8K Followers 3K Following Threat Hunter. DFIR & Malware Analyst. @sansforensics Author (FOR528) & Instructor (FOR610). Husband & father. Retro gamer too! Comments = own.

HyperDbg @HyperDbg
4K Followers 3 Following We like hypnotizing computers. #HyperDbg https://t.co/FXulXKTGjp • https://t.co/u6lVGzQpCE • https://t.co/47t9IyaiglYou might like